


©2026 Automation.com, a subsidiary of the International Society of Automation.
-
 ISA provides technical resources and standards to help industrial automation professionals advance their careers and the field. We enable automation professionals worldwide to solve problems and enhance their skills by bringing people together to create new technologies and share best practices with future automation professionals.
-
ISA Resources
-
Upcoming Events
-
Industry Insights
-
Consortia
-
ISA Global Cybersecurity Alliance
The ISA Global Cybersecurity Alliance (ISAGCA) is a collaborative forum to advance OT cybersecurity awareness, education, readiness, standardization and knowledge sharing. ISAGCA’s global ecosystem includes leaders such as Chevron, GSK, Trane Technologies, Honeywell, Johnson Controls, Schneider Electric, Rockwell Automation and Fortinet, among others. For more information, visit www.isagca.org.

230 Results Found
-
 Feature
EU Cyber Resilience Act: Multiple Routes to Compliance, One Essential Starting Point—Risk Assessment
Although the final versions of the EN 62443 standards have not been released, manufacturers can use existing standards to start preparing to comply with them. -
 News
NineTenths Joins ISASecure to Advance Adoption of ISA/IEC 62443 Cybersecurity Standards
NineTenths to promote ISA/IEC 62443 to companies in Saudi Arabia and the Gulf Cooperation Council to guide them in adopting secure, cutting-edge technologies. -
 News
ISA99 Committee Forms New Work Groups
ISA99 is forming work groups to review the effects of AI and supply chain requirements on IACS security. -
 News
OT Talent in APAC: Exploring Nontraditional Strategies and AI to Fill the Gaps
The ability to fill cybersecurity roles requires rethinking hiring strategies, investing in reskilling and implementing tools like AI. -
 News
Agilicus Joins ISA Global Cybersecurity Alliance to Accelerate Adoption of ISA/IEC 62443 Series of Standards
Agilicus and ISAGCA to work together to advance OT cybersecurity. -
 News
DeNexus Joins ISA Global Cybersecurity Alliance to Facilitate Broad Adoption of OT Cybersecurity Standards
The ISA/IEC 62443 framework, along with DeNexus’ expertise, will enable industries to assess, quantify and assign a cost to risk. -
 Feature
Securing America’s Water Systems: From Malicious Cyber Activity to Measurable Risk Reduction
Recent incidents have accelerated efforts to help water utilities improve their cybersecurity posture. One of the most significant is Project Watershed 250. -
 Feature
A Look at Two Cyber Reporting Processes: EU CRA and US CIRCIA
Cyber incident reporting is entering a new phase on both sides of the Atlantic. -
 White Paper
From Compliance to Capability: A Practical SBOM Path for Industrial Small- and Medium-Sized Enterprises
For industrial small- and medium-sized enterprises (SMEs), the real challenge is not generating a software bill of materials (SBOM) once but maintaining trustworthy software composition data that supports vulnerability decisions throughout the product lifecycle. -
 Feature
Cybersecurity in US Water Systems: Lessons from the Recent Incidents
While compliance asks, “Have we satisfied the requirement?” risk management asks, “Have we meaningfully reduced the likelihood or consequence of a cyber incident?” These rarely produce the same answer. -
 News
ISA Podcast Revisits the OT Cybersecurity Summit: Day One
The latest episode of Podomation shares highlights from the ISA OT Cybersecurity Summit, including the Cyber Empowerment Forum. -
 News
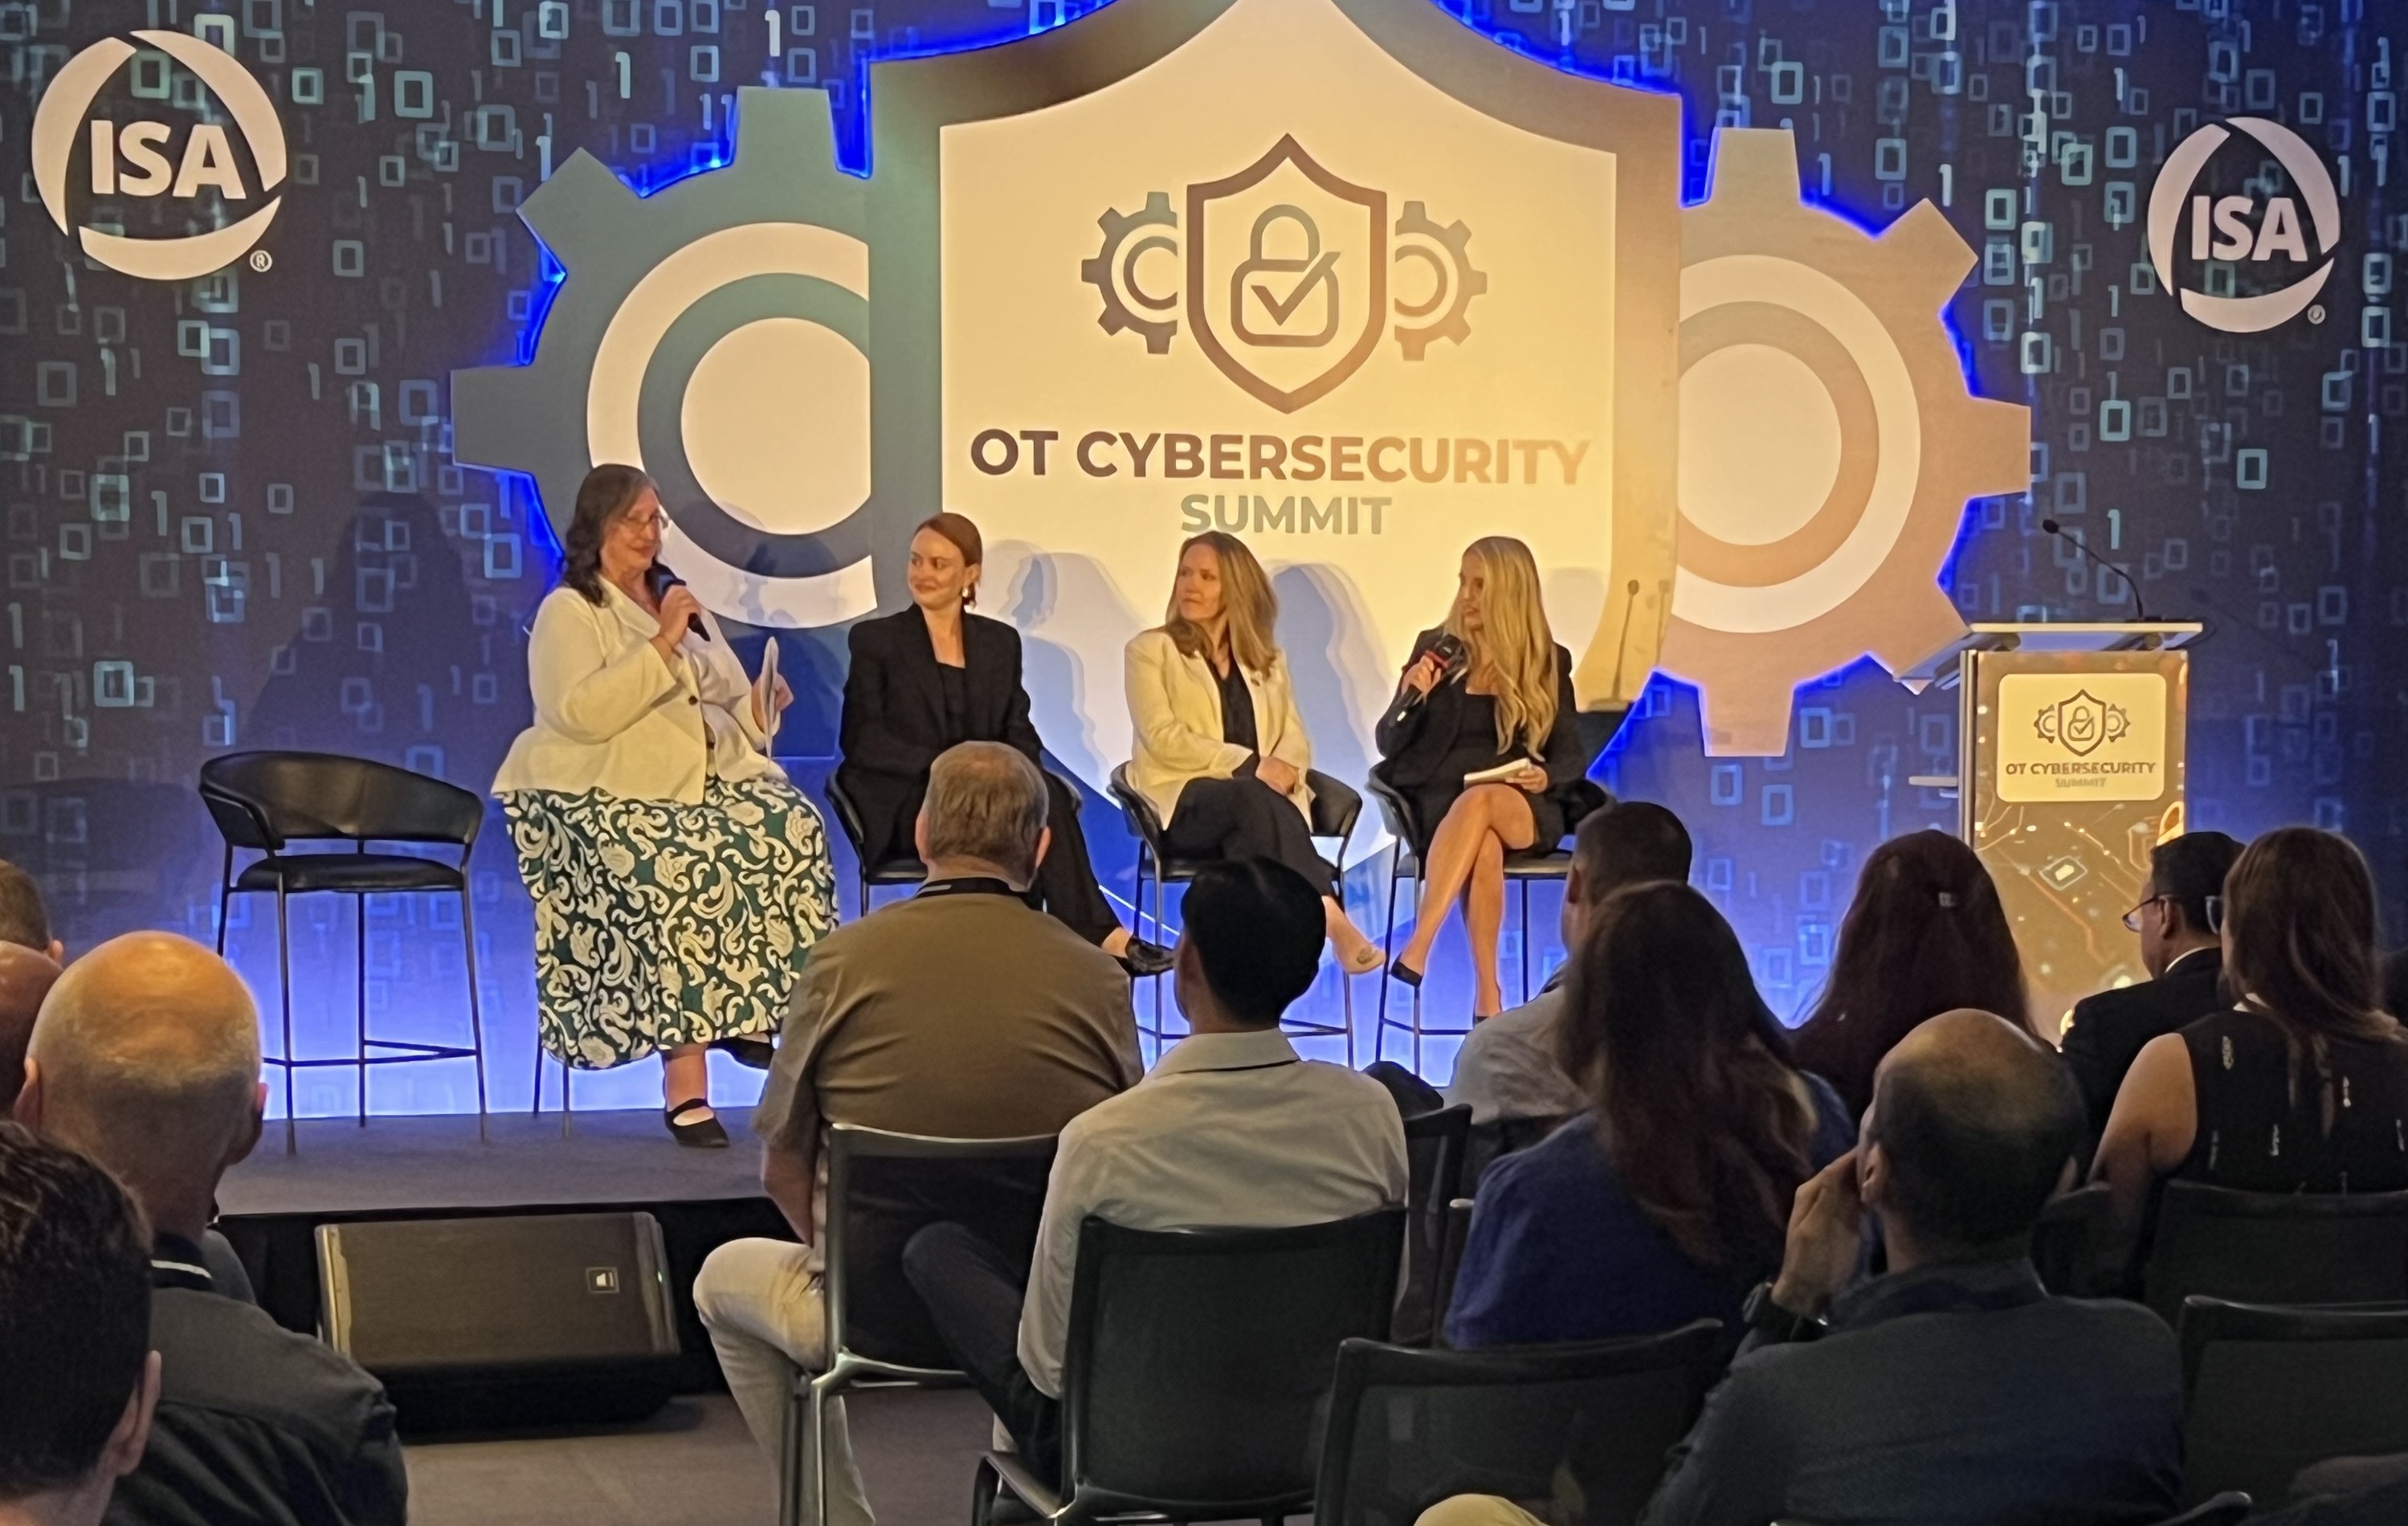
ISA OT Cybersecurity Summit Hosted in Prague for 2026
The ISA OT Cybersecurity Summit had a 25.5% increase in attendance year over year, with 314 attendees, 41 speakers and 18 sponsors and exhibitors. -
 Feature
Effective Cybersecurity Using ISA/IEC 62443
ISA/IEC 62443 provides a practical framework for aligning cybersecurity investments with operational risk, enabling organizations to build security programs that are measurable, sustainable and adaptable to changing threats. -
 Feature
Simplifying Likelihood in OT Risk Assessments: A Practical ISA/IEC 62443 Perspective
Let's discuss a practical approach to simplify likelihood assessment in OT environments by defining it as a function of access exposure and exploitability. -
 Feature
Compliant But Vulnerable: Why Cyber Resilience Is No Longer a Privilege
Morocco’s critical infrastructure operators are pushing toward digitalization. Beyond checking compliance boxes, what does it mean to have a facility that is truly cyber resilient? -
 News
ISA OT Cybersecurity Summit Delivers Training and Two Tracks of Exceptional Speakers
Attendees can learn about cyber-physical security, industrial supply chain threats and mitigation and more, as well as attend certificate training courses. -
 Feature
The Unknown Risk: Are Your OT Devices Unintentionally Visible to Malicious People?
When an OT device becomes internet-exposed — directly or indirectly — it can shift from “hard-to-reach” to “continuously discoverable” for threat actors. -
 Feature
The Human Side of Industrial Cybersecurity, and Why Consultants Align With ISA/IEC 62443
ISA/IEC 62443 brings structure to cybersecurity work in a way that reflects how industrial environments actually function, how teams of real humans collaborate and how risk is experienced in the real world. -
 Feature
Understanding and Defending Against Iranian Cyber Threats: An ISA/IEC 62443 Perspective
During the unprecedented escalation of the current 2026 cyber and kinetic war involving Iran, Israel and the United States, understanding the adversary's playbook is more critical than ever. -
 Feature
ISA/IEC 62443 in Four Practical Layers
ISA/IEC 62443 turns uncertainty into a navigable journey. -
 Feature
Announcing the OT Security Knowledge Framework: A Guide for Educators & Students, Second Edition 2025
The OT Security Knowledge Framework: A Guide for Educators & Students, Second Edition 2025 can help universities build an OT cybersecurity program. -
 Feature
Five Unique Challenges in Incident Response for Distributed Industrial Security Teams
Distributed industrial security teams protect systems where cyber incidents can have real-world consequences, often without being physically present. -
 Feature
ISA Global Cybersecurity Alliance (ISAGCA) Announces 2026 Advisory Board
The ISA Global Cybersecurity Alliance (ISAGCA) has announced members of its Advisory Board for the 2026 term. -
 Feature
Managing Shadow AI and IT in Industrial Settings
The existence of shadow AI and IT poses security risks to industry by inadvertently allowing hackers unauthorized access to sensitive systems or databases. -
 Feature
Listen: A CISO's Guide to OT Security
Chris McLaughlin's new podcast on OT cybersecurity emphasizes a collaborative approach across IT and OT. -
 Feature
How to Secure the Digital Twins of Industrial Automation
Digital twins introduce new cybersecurity challenges that can threaten both virtual systems and physical infrastructure. -
 Feature
Webinar Helps ISAGCA Community Navigate CRA and RED Requirements
FM Approvals joined ISAGCA to deliver an informative webinar called CRA and RED Explained: Compliance, Timelines and Impact. -
 Feature
The Rise of Adaptive Security: Cyber Defense in an Intelligent Age
Adaptive security leverages telemetry from endpoints, cloud workloads, network traffic and human behavior to adjust controls dynamically in real time. -
 Feature
ISA's New Position Paper Offers Stance on Industrial AI: Safety and Standards First
ISA's position paper on industrial AI outlines standards-first guidance, covering ISA/IEC 62443, operational benefits, risk and workforce upskilling. -
 Feature
Overcoming 5 Challenges in Industrial Edge Security
Understanding security challenges in industrial edge computing can help teams develop practical solutions to protect organizational data and processes. -
 Feature
7 Practical Steps to Secure Multi-AI Deployments for IoT and ICS/SCADA
Organizations can set themselves up to prioritize security even when deploying multiple AI systems in industrial settings. -
 Feature
How to Secure Digital Twins in Manufacturing
Teams must protect digital twins from cyber threats to keep production safe and running and to defend valuable intellectual property and physical assets. -
 Feature
Implementing Cyber Deception in Industrial Cybersecurity
Cyber deception strengthens security posture and reduces risk by diverting attackers away from critical assets. -
 Feature
ISA/IEC 62443 Cited in CISA OT Cybersecurity Guidance
ISA/IEC 62443 was cited in CISA's document called 'Foundations for OT Cybersecurity: Asset Inventory Guidance for Owners and Operators.' -
 Feature
Detecting AI-Generated Phishing Attacks Targeting Industrial Control System Operators
ICS operators have become increasingly frequent targets of cyberattacks. What should decision-makers incorporate into training modules for ICS operators? -
 Feature
The Cyber Resilience Act (CRA), the Radio Equipment Directive (RED) and ISA/IEC 62443: July 2025 Update
This blog post focuses on recent regulatory and standards developments impacting OT (operational technology) cybersecurity in Europe as of July 2025. -
 Feature
Defending Against Adversarial AI Attacks on Machine Vision Systems
Manufacturing lines now trust machine-vision models, but adversarial attacks may place organizations at risk. -
 Feature
Securing Manufacturing Lines from the Inside Out
As manufacturers embrace digitalization and OT convergence, their attack surface expands dramatically. -
 Feature
Understanding the Relationship Between SEMI E187 and ISA/IEC 62443 in Equipment Security Implementation
This article explores the practical relationship between SEMI E187 and ISA/IEC 62443, highlighting areas of alignment as well as nuances where the standards partially overlap. -
 Feature
Reasons to Prioritize the 2025 ISA OT Cybersecurity Summit
The 2025 International Society of Automation (ISA) OT Cybersecurity Summit in Brussels, Belgium will help you stay ahead of the curve. -
 Feature
New Resource: Comparison of ISA/IEC 62443-4-1 and NIST SP 800-218, Secure Software Development Framework
A new document from ISAGCA and ISASecure compares the ISA/IEC 62443-4-1 standard with NIST SP 800-218, Secure Software Development Framework (SSDF). -
 Feature
9 SCADA System Vulnerabilities and How to Secure Them
This blog post presents nine common SCADA system vulnerabilities as well as a few strategies to secure them. -
 Feature
Is Your OT Network Truly Secure? Here’s Why Active Directory Might Be Your Weakest Link
A single, flat Active Directory (AD) structure may expose your critical OT systems to cyber threats. -
 Feature
6 Cybersecurity Considerations When Configuring Industrial IoT Devices
Integrating industrial internet of things (IIoT) technology into industrial settings improves safety and increases productivity while introducing risks. -
 Feature
Integrating Machine Learning Techniques for Real-Time Industrial Threat Detection
Let's examine machine learning in industrial settings as applied to analyzing network data, detecting anomalies and responding to potential cyber threats. -
 Feature
Planned Plant Shutdowns: Cybersecurity Opportunities and Risks
It is essential to incorporate cybersecurity efforts into the planned plant shutdown process. -
 Feature
Confronting the OWASP Top 10 OSS Risks for Industrial Automation Control Systems
We will discuss OWASP's 2024 “Top 10 Open Source Software Security Risks” in the context of industrial automation and control systems. -
 Feature
The Role of Data Destruction in Industrial Security
How can organizations ensure appropriate data destruction practices as part of a holistic cyber-physical security program? -
 Feature
Strengthening Operational Technology Resilience: Nine Considerations
This article includes nine considerations for organizations beginning discussions around OT security and resilience. -
 Feature
Building a Skilled Workforce to Meet the Demands of OT Cybersecurity
Businesses must consider how they can implement strategies to address the OT cybersecurity skills gap.