


©2026 Automation.com, a subsidiary of the International Society of Automation.
-
 ISA provides technical resources and standards to help industrial automation professionals advance their careers and the field. We enable automation professionals worldwide to solve problems and enhance their skills by bringing people together to create new technologies and share best practices with future automation professionals.
-
ISA Resources
-
Upcoming Events
-
Industry Insights
-
Consortia
-
Navigating CRA
This column helps manufacturers, system integrators, and industrial end users understand and prepare for the European Union's Cyber Resilience Act (CRA). It features articles from industry experts, standards leaders, and practitioners. The articles explain what the CRA requires for products with digital elements, including secure-by-design development, vulnerability handling, software bills of materials, and incident reporting obligations. They also explain how the CRA relates to standards such as ISA/IEC 62443 and to regulations such as NIS2.

6 Results Found
-
 Feature
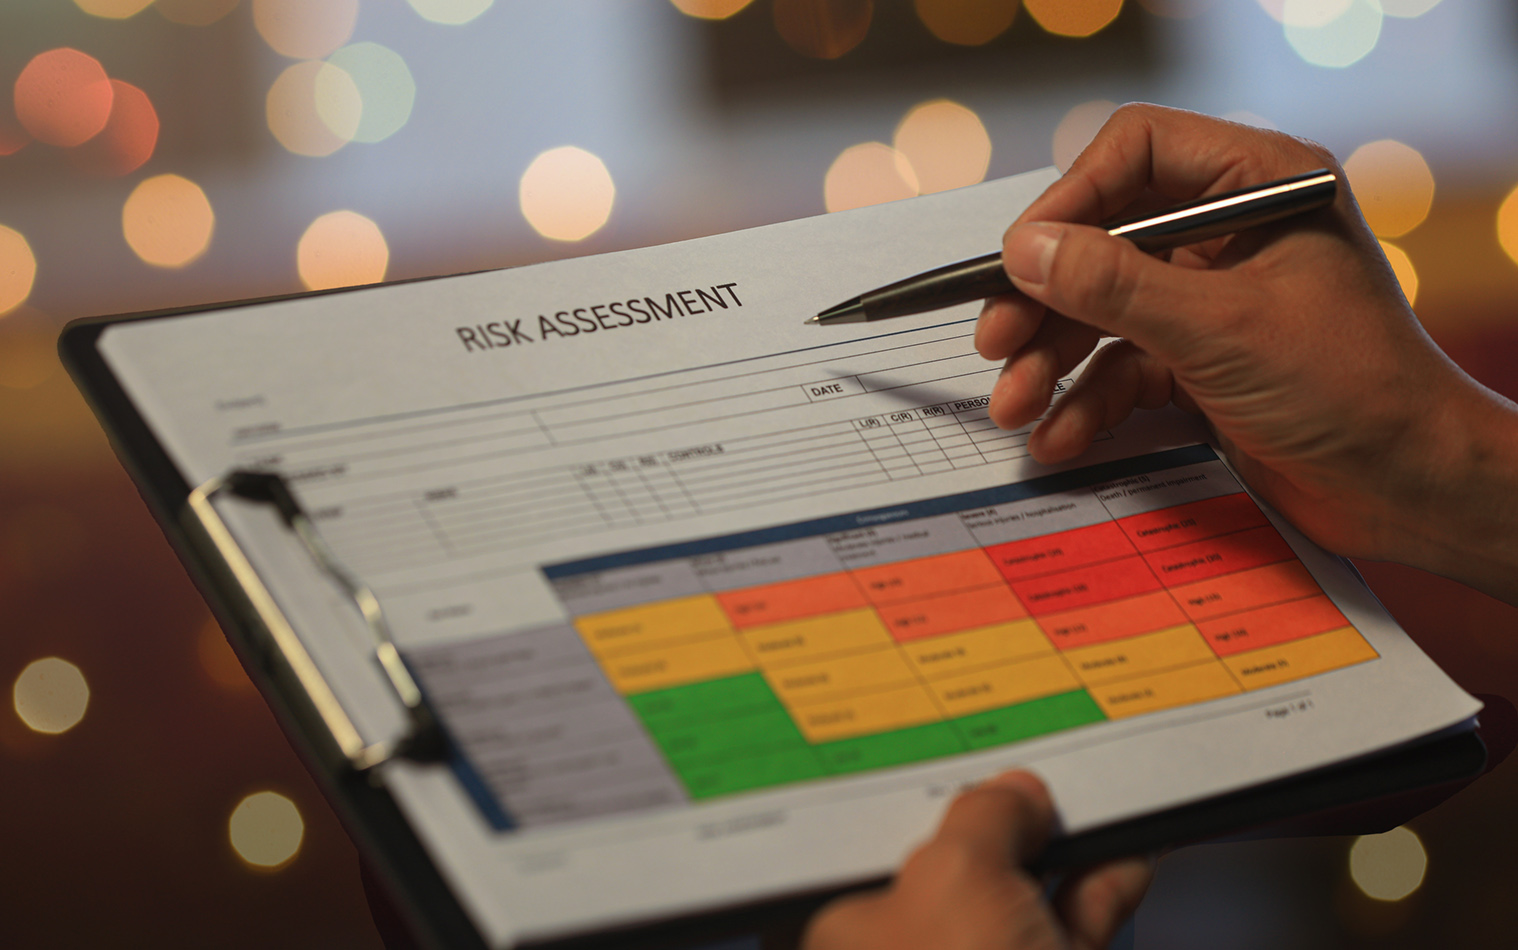
EU Cyber Resilience Act: Multiple Routes to Compliance, One Essential Starting Point—Risk Assessment
Although the final versions of the EN 62443 standards have not been released, manufacturers can use existing standards to start preparing to comply with them. -
 Opinion
The EU Cyber Resilience Act: What Does It Mean for UK Suppliers?
The CRA may influence suppliers, asset owners and customers to expect cybersecurity to become a product characteristic throughout its lifecycle. -
 Opinion
When EU Cybersecurity Regulation Crosses the Swiss Border
How will aligning Switzerland’s regulations with the CRA impact Swiss manufacturers and customers? -
 Opinion
An Opportunity for Simultaneous Business Growth and Reduction of Cybersecurity-Related Risks
Manufacturers who build ISA/IEC 62443 into their secure development lifecycle can turn the EU Cyber Resilience Act into a passport to the European market and a stronger position worldwide. -
 Opinion
The Cyber Resilience Act: Compliance Starts with Product Security, Not Documentation
Implementing the CRA is an opportunity to achieve higher levels of product security maturity by actively anticipating and preparing to address security issues that may arise throughout a product’s lifecycle.